Buy side
IT Due Diligence. Know the IT risks before you sign.
We assess your target's IT and help you bring the result into the purchase agreement.
What is IT due diligence?
From the first day after closing, your business has to run without interruption, and costs have to match the plan. IT plays a big part in both. Yet it is often overlooked in the early assessment of a company, and that gap carries over into the purchase agreement.
The risks lie, among other things, in licences with change of control clauses, in technical debt and in security gaps. They appear neither in the financial model nor in the warranties of the purchase agreement. If you only find them after closing, you can no longer negotiate them.
In scope is the target's IT, meaning the application landscape, infrastructure, IT organisation and processes, security and IT costs. We assess how well it suits the operating business and the acquisition.
Three questions you need answered before signing.
Does the target's IT fit my plans?
Using a standardised method, we review the target across all categories and show you where things get stuck.
What is a deal breaker, and what must be settled before closing?
We name the deal breakers and rank the remaining findings by importance. That makes clear what you need now and what can wait.
How do the findings get into my contract?
Together with you, we translate the findings into contract terms, from the purchase agreement to the TSA.
Our approach in three phases.
Phase 1, before signing
Target state
- Goal
- We understand what you want to achieve with the deal.
- What we do
- We go through your strategic goals. What do you want to achieve, what is special about this deal from your point of view, and what do we need to watch out for?
- Outcome
- A clear target state, derived from your strategy.
Phase 2, before signing
Analysis and risk assessment
- Goal
- You know which gaps really matter for your transaction.
- What we do
- We review and assess the target's IT as a whole. We compare the information available against a minimum standard, help you with additional requests and, where permitted, talk to the target's IT management.
- Outcome
- Named deal breakers, backed by figures wherever possible.
Phase 3, before signing
Recommendation and report
- Goal
- The findings end up where they have an effect, in the contract and in the decision paper.
- What we do
- We draw up the action plan, support you with the contract recommendations and the TSA clauses, and write the final report with an executive summary.
- Outcome
- An action plan, a report for your board and clear positions for the negotiation.
What you get.
Holistic assessment
A view of the whole IT that accompanies the deal and can be updated at any time.
Deal breakers and action plan
Use them to bring findings into the negotiation and the price, and to plan the costs coming your way in the medium term.
Contract support and final report
We support you in drafting the contract, including the clauses in the TSA, and write the final report with an executive summary for your board.
Duration and getting started.
A short initial assessment takes a few days to about two weeks. A full IT due diligence takes two to six weeks depending on the target, longer for large carve-outs and cross-border deals.
We do not wait for the data room. We are happy to start earlier, as soon as you have a target in view. We report material findings to you straight away, not only with the final report.
The outcome.
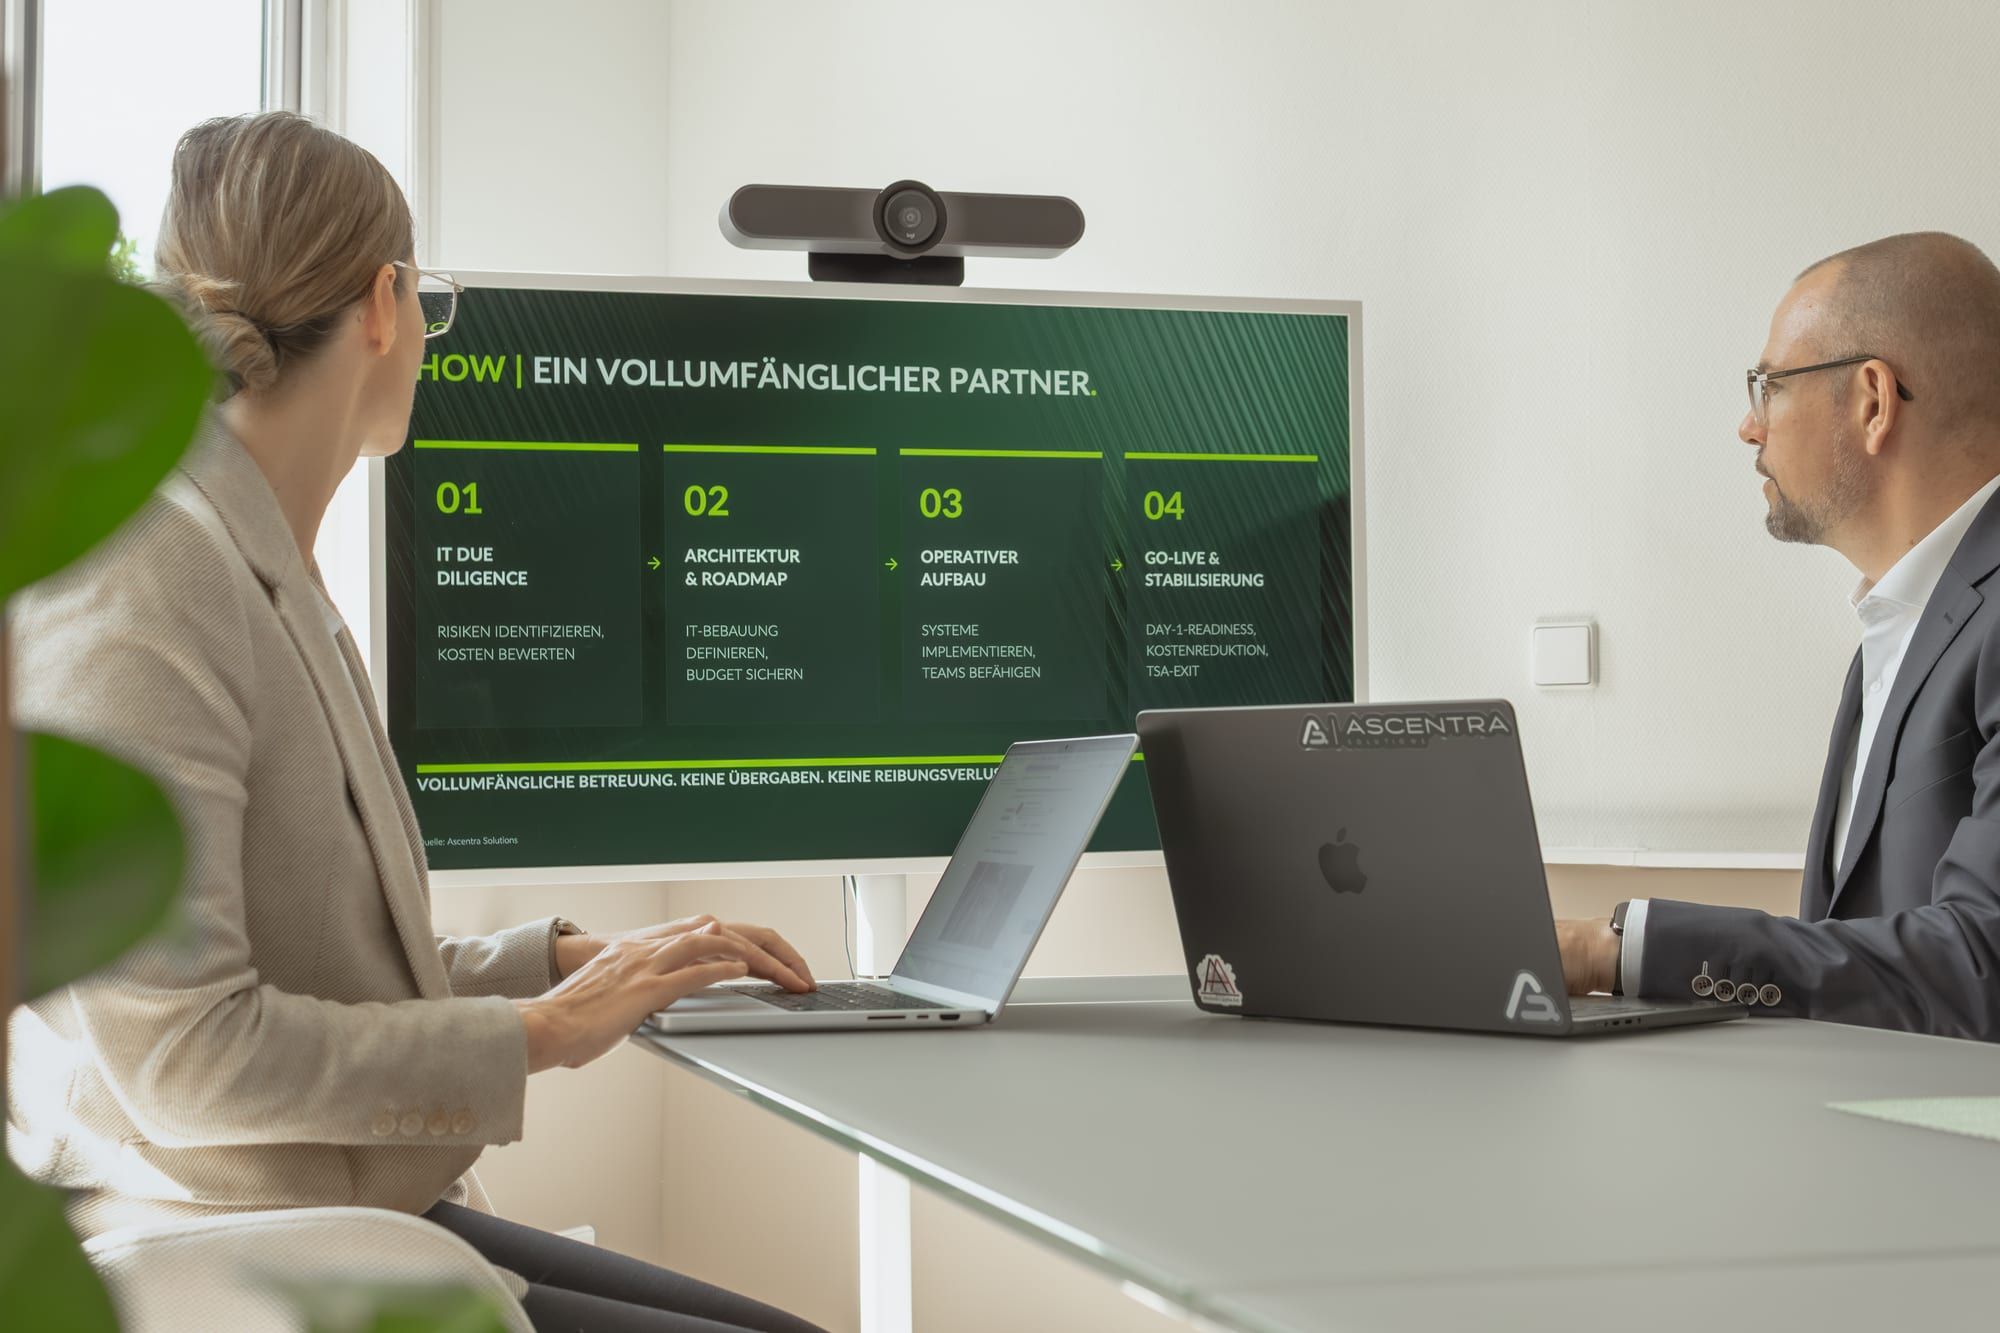
A complete assessment of your target's IT based on the information available, and an action plan you can negotiate and plan with. Where information is missing, we name the risk openly so that you can decide with your eyes open.
The difference.
We are not gone once the report is in. Every IT due diligence is set up to flow straight into delivery with our Transition Management, with the same people and no loss of knowledge.
Questions about IT Due Diligence.
How long does an IT due diligence take?
That depends above all on how IT-heavy the target is and how quickly the information becomes available. A few days are often enough for an initial assessment, while a full review takes longer. We set the timeline together at the kick-off.
When should we bring you in?
As early as possible, ideally before there is a data room. For an initial assessment, what you already know about the target is often enough. We should be on board at the latest when exclusivity begins, so that the results still feed into price and contract.
Why do you need a separate IT due diligence?
Because financial and legal due diligence usually only touch on IT. Whether the systems fit your plans, what a separation or integration will cost and how long it will take only becomes clear with a dedicated look at the IT.
Where we come in during the deal.
Milestone: Pre-deal
Milestone: Signing
Milestone: Closing
Milestone: Day 1
Milestone: TSA exit
TMI+, Buy side, View service
Mayday, On demand, View service
Talk to us about IT Due Diligence.
Pragmatic. Precise. Effective.


Your first conversation is confidential, with Andreas or Michaela. We get back to you within one working day.